
Summary
Verena Zimmermann’s core message is that cybersecurity practice should stop treating people only as the “weakest link” and instead deliberately use them as active contributors to prevention, detection, response, and recovery. After being introduced as an ETH Zurich assistant professor whose work examines security, privacy, and society, she opened by asking the audience whether humans can be the solution to cybersecurity threats. She framed the question as urgent because the threat landscape is dynamic, companies are still dealing with digitalization, AI adds new complexity, and cybersecurity professionals are scarce. Her value proposition was specific: organizations cannot rely on technology alone, so they must make better use of people, processes, and technology together.
To show that humans can strengthen security, Zimmermann used concrete cases. In 2024, a Microsoft software engineer investigated subtle SSH performance regressions, noticed unusual CPU cycles and errors, and through intensive analysis helped expose an attempted vector in compression software that had reportedly been years in the making. By warning the community quickly, he likely helped prevent a major supply chain attack. She then described a Tesla employee who was offered $1,000,000 to introduce malware but instead alerted Tesla and the authorities, helped arrest the attacker, and turned a potential insider-threat scenario into a defense success. Zimmermann also highlighted less dramatic but important everyday behaviors: reporting phishing emails, questioning strangers in the office, team leaders discussing cybersecurity, and board members making security an operational priority.
The talk then challenged the “human as problem” mindset. Zimmermann argued that assumptions about root causes determine interventions: if security teams assume incidents can be traced to one human root cause, they tend to limit user interaction, impose strict policies, and educate users mainly to reduce error. She contrasted this with the “human as liability” mindset, which recognizes that people cannot be automated away and that errors often signal a mismatch between security design and how people actually work. Passwords illustrated this point: expecting people to memorize many random complex strings does not match human cognition, so workarounds are not simply “human error” but necessary adaptation.
Zimmermann then proposed a “human as solution” mindset: not only reducing errors, but studying and fostering success, deferring to expertise beyond IT, recognizing users as workflow experts, and building resilience for recovery when things go wrong. She introduced three practical areas where this shift matters: phishing reporting, password authentication, and cybersecurity expert AI teaming. In the supplied transcript, she began the phishing-reporting example by showing how research and practice have focused heavily on clicks, sanctions, spam filters, blacklists, warnings, training, and usable design, while emphasizing that technical filters alone cannot reliably handle ambiguous emails that sit between legitimate and malicious communication.
Key Topics
5 key topics from Verena Zimmermann at ONE Conference. Thicker branches were mentioned more often in the talk.
Key Takeaways
- Engage employees as security partners, not only risk sources.
- Design security around real human workflows and cognitive limits.
- Study successful security behaviors, not only failures and clicks.
- Use technical controls while supporting human detection and reporting.
- Build resilience by involving people in response and recovery.
“Only if we engage them as partners are they willing to take this additional effort”
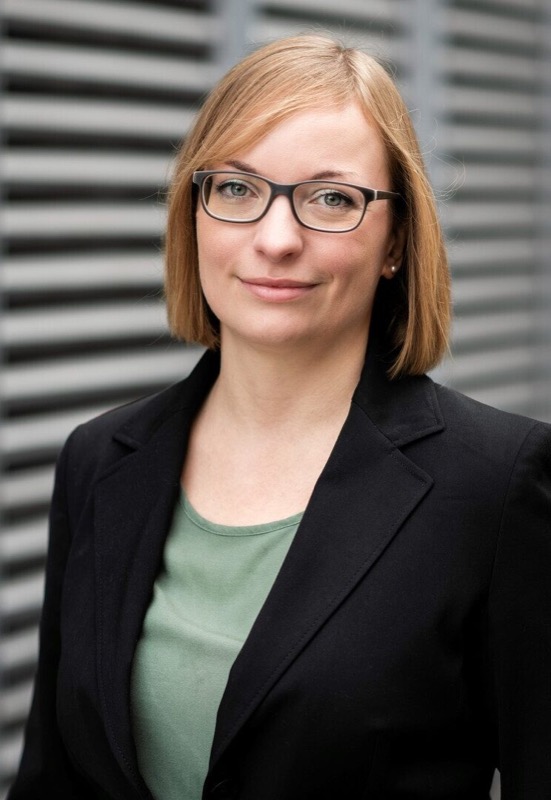
Verena Zimmermann
Assistant Professor•ETH Zurich, Department for Security, Privacy and Society
Up Next
 S
Next in agenda
Sovereignty: From Promise to Practice
Also on security culture
Humans as crucial partners in cybersecurity & resilience
Also on cybersecurity