
Summary
Stefano De Crescenzo’s core message was that Europe’s vulnerability-management infrastructure is becoming more important because the Cyber Resilience Act, rising CVE volumes, software supply-chain attacks, and AI-assisted vulnerability discovery are changing how defenders must act. Speaking from ENISA’s operational and situational awareness role, he positioned the agency as a coordinator that supports member states in cybersecurity law implementation, cyber exercises, operational cooperation, crisis networks, threat analysis, certification work, and resilience capacity such as Cyber Europe, the CSIRT network, Cyclone, and Cyber Reserve. He stressed ENISA’s mission as achieving a “high and common level of cybersecurity across Europe,” with “high” meaning quality and standards, and “common” meaning joint work with member states and stakeholders.
The session then moved into ENISA’s threat landscape findings. De Crescenzo said the 2026 threat landscape, based on analysis of 2025, did not contain surprising new categories but reinforced important patterns. Public administration remained one of the most targeted sectors by volume, partly because hacktivist groups such as No Name create many attacks against government entities. ENISA also observed intensified attacks on software supply-chain dependencies, with NPM highlighted as a heavily targeted package ecosystem because compromising upstream providers can affect many downstream packages. He described a convergence between threat-actor types, including ideologically motivated activism overlapping with state-aligned geopolitical activity, especially around Russia’s war against Ukraine and tensions in the Middle East.
AI was presented as both an existing accelerator and an emerging concern. In 2025, ENISA mainly saw AI used as a support tool: creating more convincing phishing, increasing attack velocity, and enabling automation inside networks. By 2026, however, De Crescenzo said the agentic and independent aspects of AI systems were increasingly being used to “go and hack,” a shift he described as potentially worrying if it becomes dominant. He also emphasized that the main entry points remain familiar: phishing and vulnerabilities, with particular growth in attacks against edge devices because they can provide privileged routes into networks and access-management systems.
The most detailed section focused on CVE growth and how to interpret it. ENISA saw about a 20% increase in CVEs from 2024 to 2025, and De Crescenzo cited estimates that 2026 could end with a 100% increase compared with the previous year. He argued this is not inherently bad: more CVEs can mean vendors and coordinated disclosure processes are becoming more transparent. He cautioned that vulnerability databases without CVE assignments also exist, so CVE counts do not represent all vulnerabilities. He also noted that known exploited vulnerabilities had not increased at the same exponential pace, meaning greater transparency had not yet directly translated into proportionally greater exploitation. The provided transcript ends as he begins transitioning into the Cyber Resilience Act after describing September’s surge in CVE publication, Microsoft’s Patch Tuesday, AI-supported vulnerability finding, and the resulting challenge of handling so many disclosures.
Key Topics
5 key topics from Stefano De Crescenzo at ONE Conference. Thicker branches were mentioned more often in the talk.
Key Takeaways
- Treat CVE growth as transparency, not automatically worsening security.
- Prioritize patching with risk management as CVE volumes rise.
- Monitor edge devices because attackers use them for privileged access.
- Prepare for AI-assisted exploit generation from public patch information.
- Track software supply-chain dependencies as upstream compromise risks grow.
“The fact that the CVE is not published, the vulnerability might still be there.”
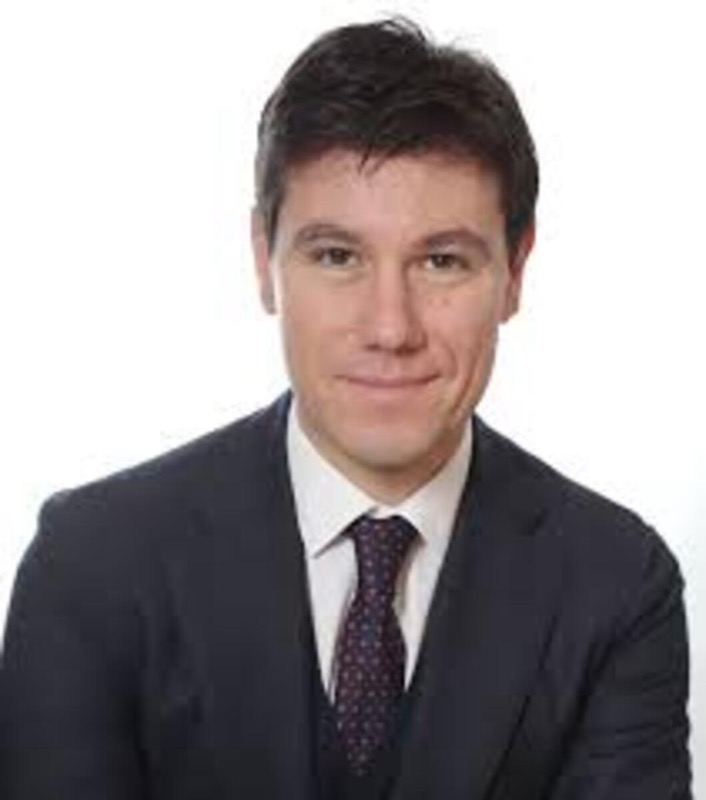
Stefano De Crescenzo
Head of Unit•European Union Agency for Cybersecurity (ENISA)
Up Next
Next in agenda
Why data protection needs a sovereign makeover
Also on cybersecurity
Opening day 2
Also on cyber resilience