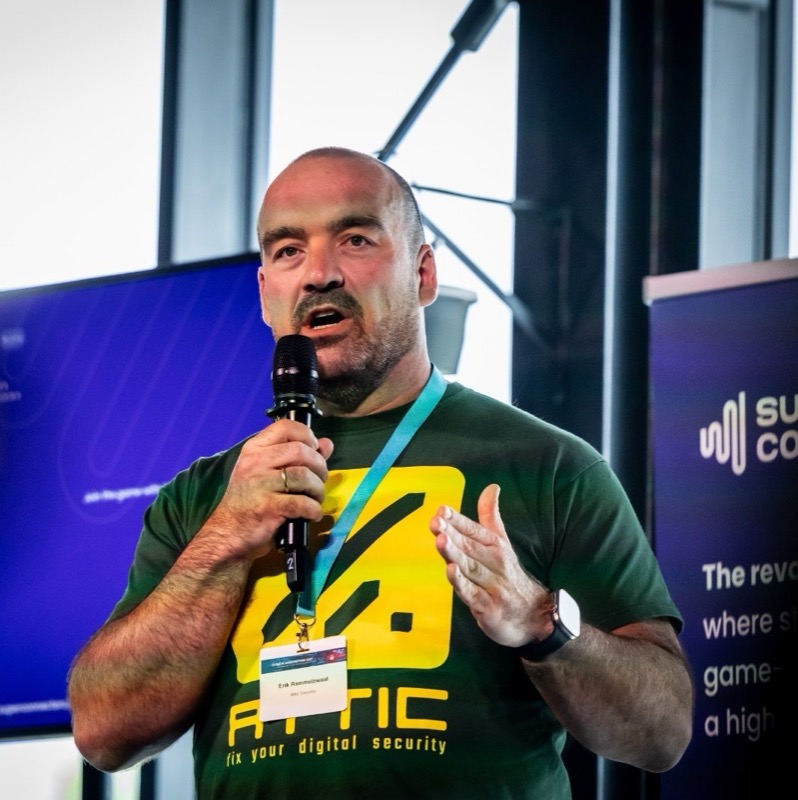
BEC Deep Dive: The New Cyclotron Technical Standard
The session’s core message was that the new Cyclotron technical standard and associated white paper are intended to give practitioners a concrete technical frame for business email compromise, with particular attention to Microsoft tenant abuse, phishing-resistant authentication, detection, and device-code related attack paths. The session opened with the moderator introducing Erik Remmelzwaal as CEO of Attic Security and co-founder of the technical white paper developed under Cyclotron. Erik then positioned the work as coming from a Cyclotron working group, with references to the NCSC, a public-private partnership context, and the Orange Cyberdefense community. Because the captured transcript is highly fragmented, many details are incomplete, but the order of topics shows a progression from organizational context into technical attack and defense material.
After the background, Erik moved into “the technique” and “the design,” referencing the platform and the idea of compromise. The talk then touched on the broader BEC ecosystem, including websites for marketplaces and access brokers, before shifting into pre-access activity described as a phishing website. From there, the session focused on Microsoft-related abuse paths, including “Microsoft exchange online direct send for tenants,” and operational sources such as printers, fax-to-email, and scan-to-email devices. These examples framed BEC not only as mailbox compromise, but as a set of email and identity pathways that can involve tenant configuration, legacy or peripheral devices, and attacker-controlled access flows.
The middle of the session emphasized authentication weaknesses and mitigations. Erik referenced desktop access, device code flow, phishing, “click fix,” and “consent fix,” then contrasted older or weaker authentication methods such as SMS, telephone authentication, and push notification defaults in Microsoft Authenticator with the stated need for phishing-resistant authentication. A concrete policy direction appeared in the discussion of a template requiring phishing-resistant multi-factor authentication for admins. He also referred to compliance-based authentication and repeated device-related terminology, suggesting a focus on tying authentication decisions to trusted or compliant devices, though the transcript does not preserve the complete explanation.
Later sections moved into BEC detection and reporting. Erik mentioned invoices, command-and-control in abbreviated form, Microsoft standard alarms, Defender, Purview compliance alarms, and Kusto Query Language in Microsoft environments. He also referred to auditing bypass and queries, indicating practical detection or investigation content. In the final part, he named device code phishing as the group’s focus, tied it to Microsoft Graph and device authentication, and pointed to GitHub as the place where technical materials from the white paper were opened. The session closed with a Microsoft note guide for token protection, device-bound protections, and “proper settings,” reinforcing that the practical conclusion was to harden Microsoft identity controls and use the published technical material for implementation.
Critical Systems and Chain Security