Summary
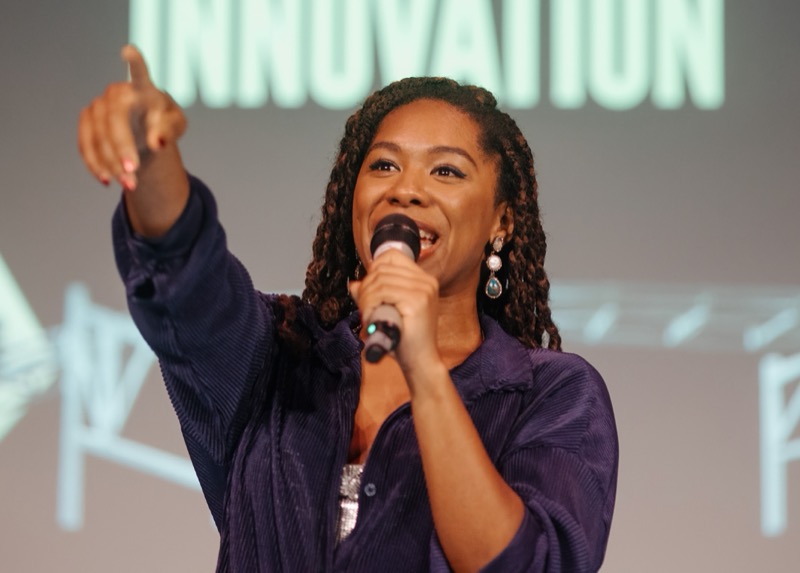
The core message of the closing session was that cyber resilience depends on active cooperation, practical information sharing, and the willingness of public and private actors to expose weaknesses before a crisis forces them to. The host first closed the loop on day one by acknowledging that attendees could not see every session, especially as many were networking or choosing between simultaneous talks. She pointed participants to the forthcoming recap hub, which would provide access to transcripts, videos, and slides where speakers had permitted sharing, so missed sessions such as “the pragmatic path to continuous purple teaming” could still be revisited.
The final guest, Eefje Zents, Director of Collaboration and Digital Resilience for the NCSC Netherlands, reflected on the day’s atmosphere of cooperation. She highlighted the nearly 2,000 visitors at the conference center and expressed hope that those left on the waiting list could be accommodated next year. She also connected the event to The Hague’s ambition to become the city of cyber security, referencing the mayor’s “house of cyber” framing and describing a useful discussion with her French colleague Geoffrey from Campus Cyber in Paris about lessons for building such an ecosystem.
Zents argued that public-private collaboration matters because no single organization has the full picture of the cyber threat landscape. Using the image of people viewing an elephant from too close, she explained that separate perspectives can be misleading unless information is shared. She then connected that need to the changed European threat environment, saying the “honeymoon phase is over” and noting that Russia is knocking on NATO’s borders physically and cyber-wise. For her, the opportunity is not to create more ecosystems but to connect existing ones, including the Cyber Resilience Network, Cyclotron, and the Anti Phishing Shield.
The most concrete example came from Ukraine. Zents described how, just before Russia’s 2022 invasion, Ukraine suffered a major DDoS attack targeting the financial sector, yet cooperation among individual banks, the Federal Bank of Ukraine, and Ukrainian National Cybersecurity Center colleagues helped restore the payment system within 24 hours. Her closing request to attendees was practical and direct: show weaknesses, share vulnerabilities, talk about incidents, and be open about mistakes so the wider ecosystem starts sharing too. The session ended with a preview of day two, including Ukrainian leaders, a new DIVD hack session, an Odido hack session, and thanks to organizers, speakers, staff, and attendees before drinks in the lobby.
Key Topics
5 key topics from Leanne Joseph and Eefje Zents at ONE Conference. Thicker branches were mentioned more often in the talk.
Key Takeaways
- Use the recap hub to catch up on missed sessions.
- Connect existing cyber ecosystems instead of duplicating them.
- Share incidents and mistakes to strengthen collective resilience.
- Train cooperation before crises, not only during attacks.
- Ask practical questions on day two’s Ukraine and hack sessions.
“Share your incidents, share your mistake, be able to speak about your mistakes because then we are able to get the party started.”