
Summary
Vaisha Bernard’s core message is that high-impact vulnerability research often starts less with elite mystique than with curiosity, persistence, and careful exploration of overlooked edges. He framed his path as a move from teenage mischief to “key collecting”: not valuing access itself, but valuing the discovery of the mechanism that unlocks it. After an introduction noting his background in Dutch intelligence, Eye Security, Black Hat speaking, and being twice named Microsoft’s most valued researcher, Bernard used stories about traffic signs, IRC, Red Hat Linux root shells, and Dungeons and Dragons alignment to explain how he redirected curiosity into ethical vulnerability research.
The Microsoft-focused story began in 2020, when he found a discrepancy in a client’s Microsoft cloud login process and submitted an elaborate report, only to receive an automated rejection saying it did not meet Microsoft’s bar. Later, while evaluating Microsoft’s phishing simulation training platform for a company product, he noticed that one of the sending domains was unregistered. He registered it and began receiving replies from real users interacting with Microsoft phishing simulations, including people asking why attachments would not load. This became his first accepted vulnerability in Microsoft’s ecosystem and established the recurring theme: important security failures can sit in plain operational details.
Bernard then described taking a week specifically to find Microsoft vulnerabilities and initially finding nothing. While procrastinating on documentation, he investigated Microsoft short links such as aka.ms and another domain, eng.ms. Logging in with his own Microsoft account unexpectedly granted access to Microsoft’s engineering hub, where searches surfaced internal references such as key vault mentions. He stopped, notified Microsoft, and traced the issue to misconfigured multi-tenant applications in Microsoft Entra. He then found 22 other internal Microsoft services with the same pattern, including an emergency broadcast system for Microsoft 365 admin centers, incident tracking for major customers, systems managing large language models such as Copilot, a sensitive risk register, security intelligence datasets, Windows source code access, and a cashback payouts tool where he could make himself administrator.
After reporting these issues, Bernard said Microsoft named him a most valuable researcher in 2025 and placed him third on a quarterly leaderboard, leading to a VIP event in Las Vegas where he felt like an impostor among deeply technical reverse engineers because, as he joked, “I logged in.” Returning from Vegas, he scanned and visited a list of 650,000 Microsoft subdomains with automation, looking beyond the original misconfiguration. He found more issues, including a Copilot development UI authentication bypass, a way to cancel Azure subscriptions by entering subscription IDs, and code execution as root in hastily deployed “vibe coded” applications that executed uploaded Python. The provided transcript ends as he begins describing what he calls the most critical vulnerability, tied to Azure Blob Storage error messages.
Key Topics
5 key topics from Vaisha Bernard at ONE Conference. Thicker branches were mentioned more often in the talk.
Key Takeaways
- Investigate small inconsistencies before assuming they are harmless.
- Stop testing and report when sensitive internal access appears.
- Scan broadly, then validate carefully to find repeated misconfigurations.
- Check cloud app tenancy settings before exposing internal services.
- Treat AI-built internal tools as high-risk until securely reviewed.
“I became a key collector instead. I became a vulnerability researcher.”
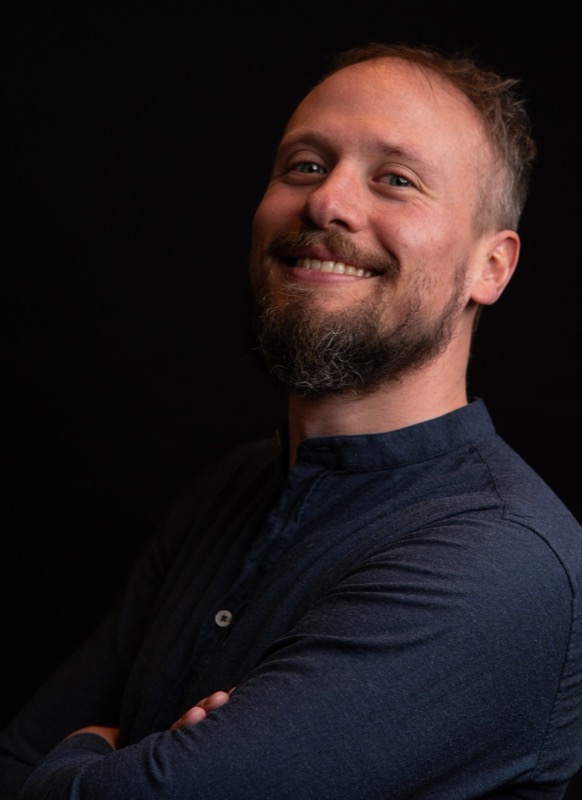
Vaisha Bernard
Chief Hacker•Eye Security
Up Next
Next in agenda
Closing day 1
 M
Also on cybersecurity
Police Hack and Pass-the-Cookie: No Crumbs, Full Access
Also on cybersecurity