
Summary
Emiel Kerpershoek’s core message was that cyber-risk awareness among small and medium-sized enterprises in The Hague region is not reliably turning into concrete protective action, and that regional, cross-sector collaboration may be needed to close that gap. Speaking as a Senior Researcher at the Center of Expertise Cyber Security at The Hague University of Applied Sciences, he positioned the session around research into SME cyber resilience. He first introduced the center’s work across cyber awareness and behavior, cyber maturity and resilience, and cybersecurity skills, then narrowed the talk to organizational resilience among SMEs.
Kerpershoek grounded the urgency in Dutch SME statistics. Drawing on 2025 figures from the Central Bureau of Statistics, he said SMEs account for 61% of value added and 75% of employment in the Netherlands, while also depending heavily on digital systems: 80% support remote working, 69% use cloud services for data storage and software, and 33% use AI technology. Despite this economic importance and digital dependency, he cited NCSC figures showing that only 29% of SMEs conduct risk assessments, 37% invest in data encryption, and only 9% provide some form of cybersecurity training. He also referenced IPSOS and TNO research indicating that 20% of employees in companies with fewer than 10 employees reported that their company had taken no specific action to increase online security.
The talk then moved from the problem to the regional response: the Platform Local Cyber Resilience The Hague, initiated in 2025 by The Hague University of Applied Sciences, the municipality of The Hague, and Connected Trust, with support from multiple umbrella organizations, trade associations, and public-private partnerships. Unlike sector-specific cyber resilience centers, this platform deliberately uses a regional and cross-sector approach, aiming to connect organizations from different sectors that face similar cybersecurity challenges and can benefit from geographical proximity. The project began with interviews among supporting partners and then launched a cyber resilience assessment among SMEs in NIS2-covered sectors such as energy, health, finance, and ICT service management, because those SMEs may face cybersecurity requirements through supply-chain relationships even if they are not directly in scope.
The main findings were sobering. Although the team approached around 1,400 organizations, used partner networks, kept the survey open for six months, attended SME conferences, and offered free reports with improvement recommendations, the final response was only 50 organizations. Kerpershoek treated this low response not merely as a research limitation but as a finding in itself: SMEs are very hard to engage on cyber resilience, and trade associations reported similar struggles. Among participating non-IT and non-cyber SMEs, 75% had not delegated cybersecurity roles or responsibilities, and more than 80% had not fully implemented basic controls such as vulnerability assessments, backups, updates, and secure settings. At the same time, only 50% were somewhat to very concerned about cyber impact, while they rated their own cyber resilience at an average of 84%, suggesting a mismatch between perceived and actual preparedness.
Key Topics
5 key topics from Emiel Kerpershoek at ONE Conference. Thicker branches were mentioned more often in the talk.
Key Takeaways
- Prioritize basic cybersecurity controls before advanced resilience initiatives.
- Assign clear cyber roles and responsibilities inside SMEs.
- Engage SMEs through regional, cross-sector collaboration networks.
- Use assessments to generate practical recommendations and recruit participation.
- Address overconfidence by comparing perceived resilience with actual controls.
“awareness of these risks can be translated into action on account of the SMEs.”
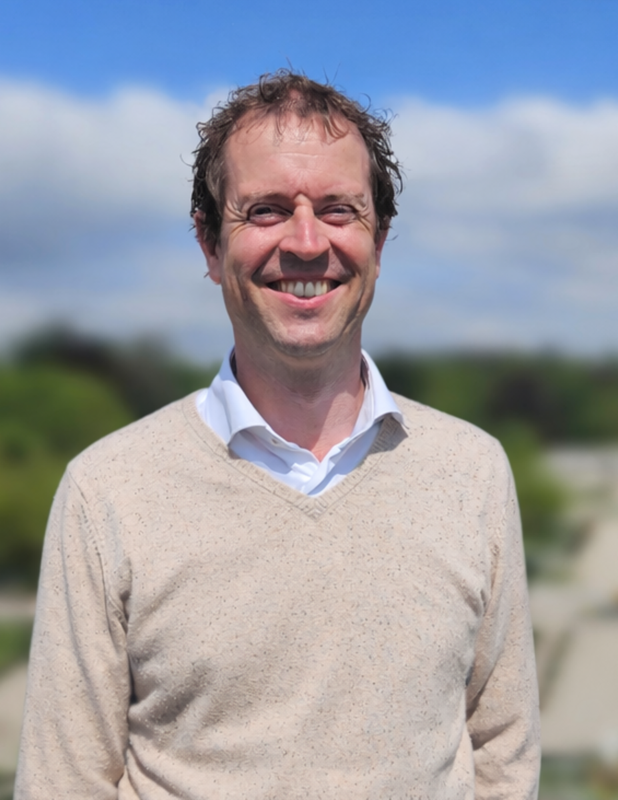
Emiel Kerpershoek
Sr researcher Cyber Security•The Hague University of Applied Sciences
Up Next
Next in agenda
AI: The Myth(os), truths, and what to do’s
Also on nis2
Aligning NIS2 in Practice Across the EU
Dániel Váczi
Also on nis2