
Summary
Dany Alwetzi’s core message was that practical NIS2 compliance across the EU is not a single, uniform exercise: organizations, especially international company groups, need to understand how each member state has transposed the directive before budgeting, assigning responsibility, or reusing compliance work. Speaking from the perspective of a startup building a platform for the NIS2 ecosystem, he framed the session around the gap between the EU-level directive and the operational reality inside affected organizations. He opened with audience polling on countries represented, attendee roles, and AI usage, noting that most participants appeared to be consultants and that AI had changed the cybersecurity consultancy and audit landscape significantly in the previous half year.
The presentation then moved through the current implementation landscape. Alwetzi emphasized that even where countries appear “green” on implementation maps, this does not always mean practical enforcement or organizational work has started. He used Hungary as a recurring example: Hungary was an early adopter, with its first NIS2 law enforced in 2023 and already a second law in place, but he described its implementation as unusually complex. He contrasted this with countries such as the Netherlands, where enforcement timing differed, and France, where he said the status could appear implemented while still not being fully enforced. His broader point was that international CISOs cannot assume that an EU-wide NIS2 program will fit every subsidiary; local triggers, deadlines, and legal details matter.
A major section focused on differences in national approaches to controls, evidence, audits, and certification. Some countries use EU-oriented control sets, while others rely on their own frameworks or standards, including ISO 27k, Belgium’s CyFun-style approach, and Hungary’s NIST 800-53-based model. Alwetzi stressed that Hungary’s model can require companies to assess more than 1,400 controls and undergo mandatory third-party audits, which can turn compliance from a few-month ISO-style effort into work lasting more than a year. He also noted differences in audit cycles, such as two-year periods in Hungary and Croatia versus three-year periods in Poland and Latvia, and pointed out that even incident reporting can vary by country despite being defined in the NIS2 directive.
The closing visible portion shifted from legal fragmentation to operational response. Alwetzi described two customer mindsets: organizations wanting a “green button” for compliance and more mature organizations trying to convert NIS2 work into real resilience. He connected this to AI adoption, explaining that customers and auditor partners had begun asking why AI was not integrated into compliance platforms. His example was policy generation: tools such as ChatGPT or Gemini can provide a useful base if sensitive information is masked properly, but he cautioned that generated output will not automatically become the organization’s final policy.
Key Topics
5 key topics from Dániel Váczi at ONE Conference. Thicker branches were mentioned more often in the talk.
Key Takeaways
- Map each subsidiary’s national NIS2 triggers before launching work.
- Budget more for countries requiring mandatory third-party audits.
- Reuse evidence collection across countries to reduce repetitive compliance work.
- Validate ISO 27k assumptions against each national NIS2 law.
- Mask sensitive data before using AI for policy drafting.
“The most interesting, how international companies should work with whole chaos, I would say.”
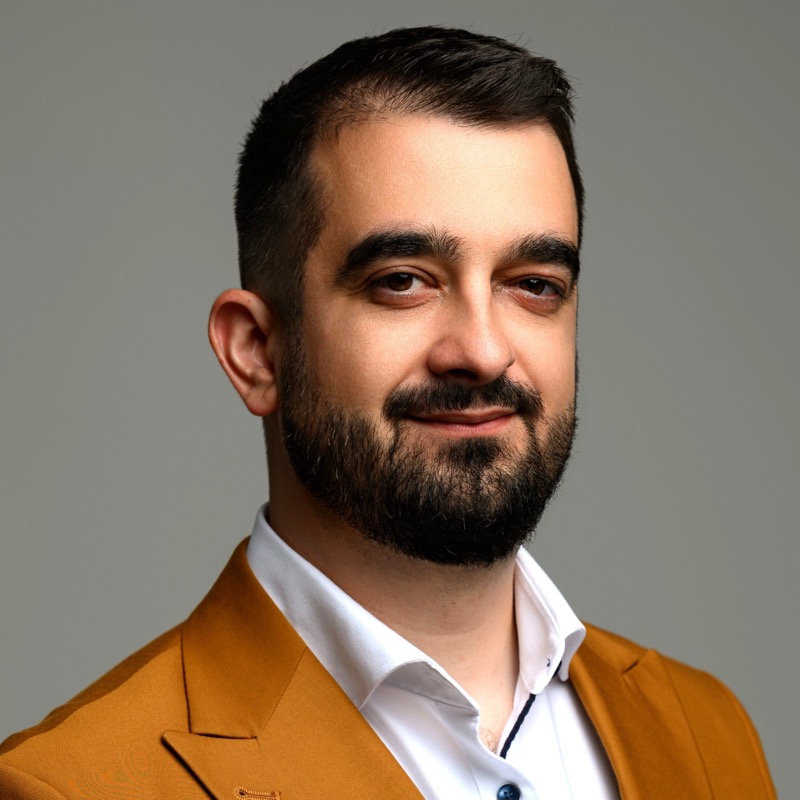
Dániel Váczi
CEO•Brind
Up Next
Next in agenda
Vishing At Scale: Humans vs. Voice Agents
Indy Mellink
Also on nis2
IDRS report demonstrates cyber resilience for NIS2/DORA
Also on cyber resilience
From awareness to action: SME Cyber Security
Emiel Kerpershoek