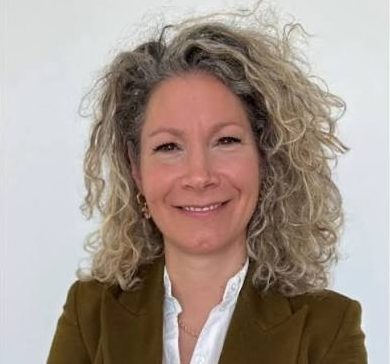
Eefje Zents
Director of Resilience & Chief Relations Officer
Sessions (2)
Sessions featuring Eefje Zents at ONE Conference
International Perspectives on NCSC-NL’s CCB Program
The core message of the provided transcript is that cyber capacity building succeeds when it creates durable local capability, trusted partnerships, and ecosystem-wide resilience rather than one-off technology transfer. Danny Jaspers opened by defining Cyber Capacity Building within the Dutch Cybersecurity Center as partnership with countries to help them become more cyber resilient through knowledge sharing, partnerships, and training. He framed the session around three blocks: international missions and lessons learned, collaboration partnerships, and sustainable cyber capacity building, with audience questions after each block and a broader Q&A at the end. Emilia Nghikembua, head of Namibia’s NCSC/Cyber Incident Response Team and the ICT regulator, explained why Namibia’s experience made the topic practical rather than abstract. When Namibia began developing its CERT, the challenge was not only establishing a national team but building the surrounding cybersecurity ecosystem. She listed the needs: specialist skills, incident response capabilities, governance, technical tools, credible threat intelligence, and partnerships. International cooperation, including the partnership with NCSC-NL, helped through operational guidance, knowledge transfer, technical support, and continued engagement. After about two years of operation, Namibia’s CERT now supports incident coordination, threat monitoring, information sharing, awareness, and connections to Southern Africa CERT, Africa CERT, and FIRST. Velimir Radicevic of FIRST positioned FIRST as an enabling layer above a living community of security teams, including NCSC-NL and Namibia’s CSIRT. He argued that cyber capacity building is at a crossroads: the issue is not only resource constraints, but a long-standing preference for efficiency over effectiveness. In his view, CCB has too often been treated as short sprints, when it is actually a long, complex, multifaceted, human-driven marathon requiring partners to stay present beyond budgetary cycles. Eefje of the Dutch Cybersecurity Center connected international resilience directly to Dutch and European resilience, while Pieter van den Berg of the Dutch Ministry of Foreign Affairs described cyber capacity building as one pillar alongside diplomatic responses to cyber threats and norm-setting discussions on state behavior in cyberspace. In the first substantive exchange, Emilia emphasized that focusing only on the CERT is insufficient: the whole ecosystem must be capacitated and resilient. She cited practical incident causes such as expired passwords and outdated SSL certificates to show why organizations beyond the national CERT need capability. Danny then referenced a February 2024 training mission in Namibia that began as a one-week visit by consultants but evolved into biweekly online advice and consultation. Emilia said this continuity was necessary because threat intelligence can become outdated quickly, and sustainable engagement is the only way to keep knowledge from becoming obsolete. The provided transcript ends around the point where Eefje begins elaborating on how Namibia’s experience also strengthens NCSC-NL’s own approach.
Closing day 1
The core message of the closing session was that cyber resilience depends on active cooperation, practical information sharing, and the willingness of public and private actors to expose weaknesses before a crisis forces them to. The host first closed the loop on day one by acknowledging that attendees could not see every session, especially as many were networking or choosing between simultaneous talks. She pointed participants to the forthcoming recap hub, which would provide access to transcripts, videos, and slides where speakers had permitted sharing, so missed sessions such as “the pragmatic path to continuous purple teaming” could still be revisited. The final guest, Eefje Zents, Director of Collaboration and Digital Resilience for the NCSC Netherlands, reflected on the day’s atmosphere of cooperation. She highlighted the nearly 2,000 visitors at the conference center and expressed hope that those left on the waiting list could be accommodated next year. She also connected the event to The Hague’s ambition to become the city of cyber security, referencing the mayor’s “house of cyber” framing and describing a useful discussion with her French colleague Geoffrey from Campus Cyber in Paris about lessons for building such an ecosystem. Zents argued that public-private collaboration matters because no single organization has the full picture of the cyber threat landscape. Using the image of people viewing an elephant from too close, she explained that separate perspectives can be misleading unless information is shared. She then connected that need to the changed European threat environment, saying the “honeymoon phase is over” and noting that Russia is knocking on NATO’s borders physically and cyber-wise. For her, the opportunity is not to create more ecosystems but to connect existing ones, including the Cyber Resilience Network, Cyclotron, and the Anti Phishing Shield. The most concrete example came from Ukraine. Zents described how, just before Russia’s 2022 invasion, Ukraine suffered a major DDoS attack targeting the financial sector, yet cooperation among individual banks, the Federal Bank of Ukraine, and Ukrainian National Cybersecurity Center colleagues helped restore the payment system within 24 hours. Her closing request to attendees was practical and direct: show weaknesses, share vulnerabilities, talk about incidents, and be open about mistakes so the wider ecosystem starts sharing too. The session ended with a preview of day two, including Ukrainian leaders, a new DIVD hack session, an Odido hack session, and thanks to organizers, speakers, staff, and attendees before drinks in the lobby.